⚡ Quick Answer
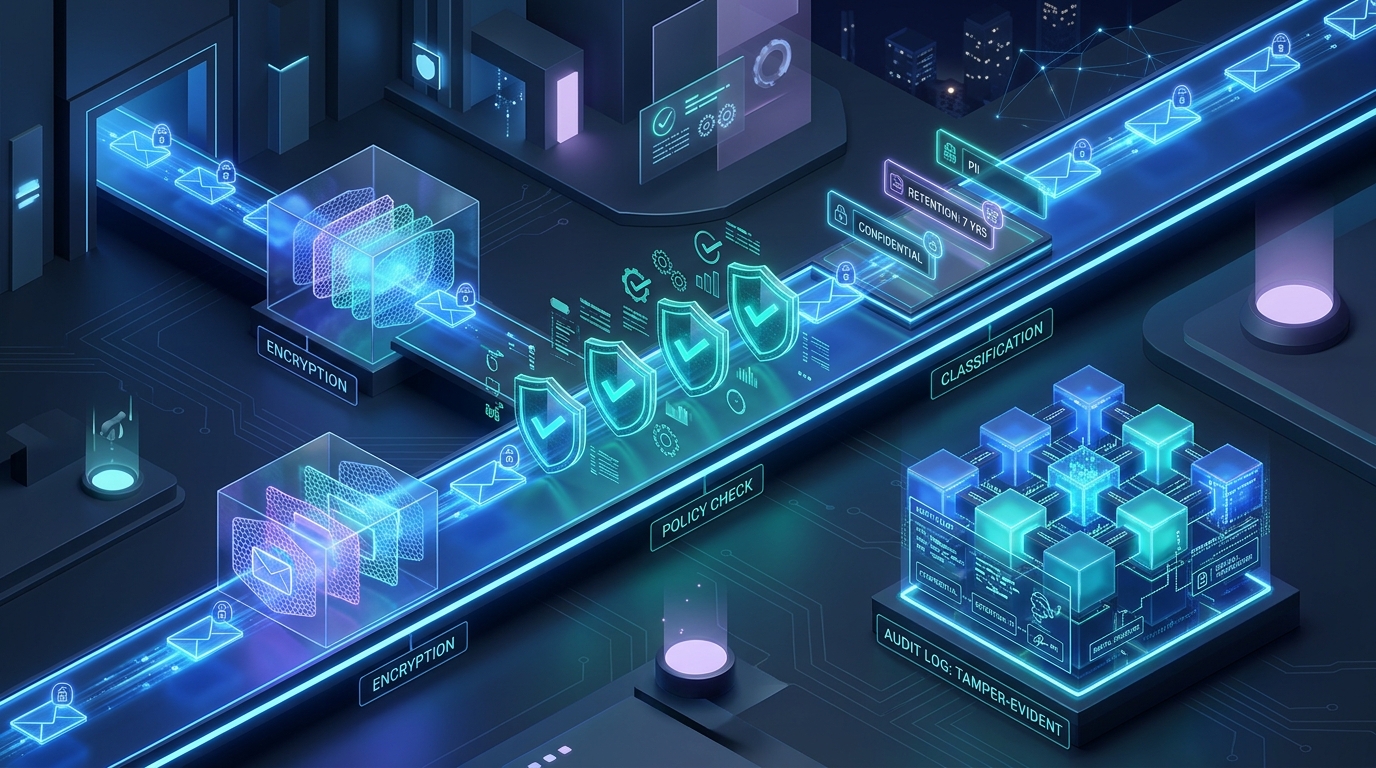
Email compliance software is a system that monitors, controls, classifies and records business email so an organization can follow laws such as SEC Rule 17a-4, HIPAA, GDPR and SOX, and prove it to an auditor. It applies policy to messages before and after they are sent, and it keeps a tamper-evident record of every decision it makes.
That is the short version. The rest of this guide covers what the software actually does, which regulations drive the requirement, the features worth paying for, how deployment works, and how to avoid the mistakes that make compliance projects stall.
Table of Contents
- What is email compliance software?
- Two meanings of 'email compliance'
- Why email is still the biggest compliance exposure
- Regulations that drive email compliance
- What email compliance software actually does
- Storage is not the same as a defensible audit trail
- How email compliance software works
- Deployment options
- Who needs it: industry use cases
- Features to look for when buying
- Questions to ask every vendor
- Common mistakes
- Implementation roadmap (90-Day Plan)
- What does it cost?
- How it differs from related tools
- How MailGovern approaches email compliance
- Frequently asked questions
What is email compliance software?
Email is still where most business gets done. Contracts are negotiated in it, customer data travels through it, and employees make decisions in it every minute of the day. That also makes it the place where regulated information leaks, records go missing and policies get ignored.
Email compliance software sits between your mail platform and your regulatory obligations. It does three essential jobs:
- Prevent. Stop or flag messages that break policy, such as sensitive data going to the wrong recipient.
- Organize. Classify messages by type, sensitivity or regulatory category so the right rules apply to the right mail.
- Prove. Keep a searchable, tamper-evident audit trail showing what happened to each message and why.
If you want to see how this looks as a full platform, the MailGovern email compliance software page walks through each capability in detail.
Two meanings of 'email compliance'
The phrase is used for two very different problems, and the tools are not interchangeable:
- Marketing email compliance: Following rules for commercial messages—such as CAN-SPAM in the US, CASL in Canada, and consent requirements under GDPR. This centers on unsubscribe links, honest headers, and proof of opt-in consent. Email marketing platforms usually handle it.
- Enterprise communication compliance: Governing everyday business email—who can send what, what must be retained, what must be supervised, and what must be produced in an investigation. This is the focus of this guide.
If you run marketing campaigns, check your sending platform for the first. If you work in compliance, legal, IT or security, the second is almost certainly your problem.
Why email is still the biggest compliance exposure
New channels get attention, but email remains the system of record for most regulated businesses. Three realities keep it uniquely risky:
- Volume and speed: A single employee can send hundreds of messages a day. Nobody reviews them one by one, so the risk lives in the tail: the one message with a patient record, a client list, or an unreleased earnings figure.
- Human error: Misdirected emails, reply-all mistakes, wrong attachments, and autocomplete accidents are rarely malicious, but regulators treat the resulting data exposure the same way.
- Records obligations: Many rules do not only ask you to protect email. They ask you to keep it, supervise it, and retrieve it on demand. Missing or incomplete records are a violation on their own, even if nothing harmful was ever sent.
Regulations that drive email compliance
Which rules apply depends on your industry and geography. This table is a starting point, not formal legal advice. Confirm specifics with your compliance counsel.
A few of these deserve a closer look:
- SEC and FINRA care heavily about retention and supervision. The SEC has issued billions in penalties against firms for failing to preserve business communications, which is why financial teams treat email records as a board-level topic.
- HIPAA is less about multi-year retention and more about protecting patient information in transit and proving who accessed it.
- GDPR adds a strict breach clock. If personal data is exposed, you may have just 72 hours to notify the supervisory authority, which is nearly impossible to meet without logs that tell you exactly what was sent and to whom.
- SOX raises the stakes on records integrity: communications that can be edited or quietly deleted represent acute liability.
What email compliance software actually does
Feature sets vary across tools, but a serious platform covers eight core areas:
- Policy enforcement and blocking: Checks messages against rules you define, such as blocking outbound mail containing account numbers, or holding messages addressed to unapproved external domains. Leading platforms let you block, quarantine, redirect, or tag based on risk severity.
- Classification: Every message is categorized: contract, client instruction, health data, internal conversation, or spam. Classification is what lets you apply distinct retention, review, and access rules. Modern solutions combine deterministic regex rules for structured data with AI for conversational context.
- Workflow automation: Once a message is classified, automatic actions take place: route to a supervisor, alert a compliance officer, move to a folder, append tags, or trigger external systems via webhooks—without requiring manual inbox triage.
- Retention and archiving: Retains mail for as long as each mandate requires and safely disposes of it afterward. Retention schedules vary by regulation and document type, so multi-schedule support is mandatory.
- Audit trail: The defining capability separating compliance software from basic storage. An audit trail records message receipt, classification tags, triggered rules, subsequent actions, and access history.
- Supervision and monitoring: Regulated organizations must prove ongoing oversight. Platforms provide dedicated review queues, escalation workflows, and non-repudiable logs of reviewer activity.
- Search, legal hold and eDiscovery: When an investigation strikes, legal hold freezes automatic deletion schedules. Fast, indexed search and bulk export produce defensible records promptly.
- Reporting: Executive dashboards and exportable audit reports let compliance teams substantiate control effectiveness to auditors and boards without manually compiling spreadsheets.
Storage is not the same as a defensible audit trail
Many organizations believe they are covered simply because their mailboxes are backed up or stored in a generic cloud archive. That confuses two fundamentally different things:
Storage answers the basic question: do we still have this message?
A defensible audit trail answers the questions examiners ask: was the compliance policy applied, when, by what exact rule, with what outcome, and can you prove the record was never altered afterward?
A regulator or opposing counsel will focus on the second set of questions. If all you can produce is a folder of raw messages, you have evidence that email existed, not evidence that you governed it. This gap is why the category is increasingly called communication governance. To understand how policy, accountability, and technical controls integrate, read our guide to email governance.
How email compliance software works
While architectures differ, the operational flow generally follows five steps:
Two design principles are crucial here: First, deterministic rules should always precede AI, ensuring predictable messages are processed with absolute consistency. Second, the log must record the decision rationale alongside the message, because examiners evaluate how decisions were reached.
Deployment options
Where the software runs directly affects security audits, operational cost, and deployment speed:
- Cloud mail platforms: For Microsoft 365, native API-level integration is the standard. See how MailGovern handles Exchange Online compliance. For Google environments, see Google Workspace email compliance.
- On-premise mail servers: Many financial institutions, healthcare networks, and government entities maintain self-hosted infrastructure for data sovereignty. Ensure your provider offers native support for on-premise Exchange Server rather than assuming cloud-only tools will work.
- Client-side add-ins: An Outlook add-in warns employees at the moment of composition, catching sensitive leaks or misdirected sends before transmission occurs.
- White-label: CRM, ERP, and legal tech providers can embed compliance capabilities directly into customer-facing applications instead of building custom archiving infrastructure.
Who needs it: industry use cases
- Financial services: Mandatory retention, supervisory queues, and production under SEC and FINRA mandates. Misdirected client financial data is a constant threat. See our email compliance software for financial services guide.
- Healthcare: Preventing protected health information (PHI) from egressing via unencrypted or incorrect addresses, and evidencing access control.
- Legal: Protecting attorney-client privilege, maintaining client confidentiality, and executing bulletproof legal holds without risk of spoliation sanctions.
- Insurance: Retaining claims discussions, underwriting documents, and policyholder records across disparate regional jurisdictions.
- Government and public sector: Public records acts, FOIA compliance, strict data residency requirements, and retention mandates.
- Pharma and life sciences: Preserving clinical trial communications, regulatory correspondence, and quality assurance exchanges.
Features to look for when buying
Use this evaluation matrix when scoring prospective vendors:
- ✓ Dual-engine classification (deterministic rule baseline + contextual AI with confidence thresholds)
- ✓ Visual workflow builder with multi-action branching (block, quarantine, reroute, tag, notify, webhook)
- ✓ Immutable, tamper-evident audit ledger capturing decisions and reviewer rationale
- ✓ Granular retention schedules configurable by regulatory mandate and document category
- ✓ Instant legal hold triggers with cross-mailbox search and rapid eDiscovery export
- ✓ Role-based access control (RBAC) separating administrative privileges from auditor read-only access
- ✓ Native connectors for Microsoft 365, Google Workspace, and on-premise Exchange
- ✓ Robust REST APIs for feeding compliance telemetry into SIEM, SOAR, and GRC systems
- ✓ Comprehensive error handling and transparent logging of sync state and warning conditions
- ✓ Flexible hosting options: SaaS, hybrid on-premise, or private cloud
- ✓ Audit-ready reporting tailored for regulatory examiners and board governance committees
Questions to ask every vendor
- Can you walk through the complete audit trail for a single email from receipt to final disposition?
- How do you technically prove that retained messages and logs have not been altered or deleted?
- What occurs when the AI engine is uncertain about a message's classification?
- Which email platforms do you support natively via API, and which require journal rules or mail routing workarounds?
- Where is our archive data physically hosted, and can we designate our geographic storage region?
- How are retention policies updated, and is there an audit record of policy changes?
- What happens to inbound and outbound messages if an API outage or connectivity failure occurs?
- How does your platform support our specific regulatory requirements, rather than generic retention?
- What does the typical implementation timeline look like, and who handles configuration?
- What is the total three-year cost of ownership, including data ingestion, storage tiers, user licensing, and support?
Common mistakes
- Treating compliance as a storage project: Archiving only stores past mail. Without proactive policy enforcement, outbound supervision, and audit logging, you have simply centralized your liability.
- Setting rules once and never reviewing them: Business operations and regulations evolve constantly. Unreviewed rules generate noise, rule drift, and blind spots. Establish quarterly rule reviews.
- Over-blocking and frustrating users: If policies disrupt daily work too aggressively, employees will circumvent controls using personal webmail or shadow messaging apps. Start in audit/tag mode and tune thresholds before enforcing hard blocks.
- Neglecting on-premise and hybrid systems: Regulators examine your entire environment. Partial compliance coverage creates dangerous exam vulnerabilities.
- Neglecting user training: Users who understand why an email was quarantined cooperate. Users who are left in the dark flood the IT help desk with support tickets.
- Selecting tooling without legal and compliance: While IT implements the platform, legal and compliance stakeholders must defend it in audits and depositions. Involve them early.
Implementation roadmap (90-Day Plan)
Days 1 to 30: Scope and Connect
- Map applicable regulations (SEC, HIPAA, GDPR, SOX) and their respective record classes.
- Identify mailboxes, user tiers, and communication channels in scope.
- Connect mail environments natively and run policies in monitor-only (passive) mode.
Days 31 to 60: Tune and Test
- Build classification rules for top high-risk scenarios (PII, financial statements, contracts).
- Validate AI classification against sample datasets and calibrate confidence cutoffs.
- Establish automated routing workflows for compliance officer review and escalation.
Days 61 to 90: Enforce and Prove
- Activate real-time blocking and quarantine workflows for validated high-risk policies.
- Finalize retention schedules and operationalize legal hold procedures.
- Conduct a mock regulatory audit: extract five arbitrary messages and trace their lifecycle end to end.
Following Day 90, institutionalize monthly compliance incident reviews and quarterly rule audits.
What does it cost?
Pricing models vary across the market. The primary drivers are active mailbox count, processing throughput, retention duration, AI usage tiers, hosting model, and support SLAs. When calculating investment, evaluate the full three-year total cost of ownership (TCO), including the labor required to manage false-positive alerts.
The true return on investment (ROI) is primarily risk mitigation and time saved: avoiding multi-million-dollar regulatory fines, mitigating breach disclosures, answering eDiscovery subpoenas in hours rather than weeks, and eliminating manual evidence compilation.
How it differs from related tools
Compliance software is frequently confused with surrounding security and infrastructure tooling. Here is how they compare:
How MailGovern approaches email compliance
MailGovern is built on three core pillars: Block, Classify, and Workflow. Deterministic policy rules execute first, context-aware AI classifies edge cases, and automated workflows route, quarantine, or escalate with every action recorded to an immutable audit trail.
MailGovern supports Microsoft 365, on-premise Exchange Server, and Google Workspace, offering SaaS, private on-premise, or white-label deployment. The objective is clear: not simply to store email, but to prove exactly how every communication was governed.
Frequently asked questions
What is email compliance software?
It is software that monitors, controls, classifies and records business email so an organization can meet legal and regulatory requirements and prove it with an audit trail.
Is email compliance software the same as email archiving?
No. Archiving stores messages. Compliance software also enforces policy, automates actions and records the decisions made on each message.
Which industries need it most?
Financial services, healthcare, legal, insurance, government and pharma face the most direct requirements, but any company handling personal data, payment data or audit records can benefit.
Does it work with Microsoft 365 and Google Workspace?
Most modern platforms do. Check for native support for your exact environment, including on-premise Exchange if you still run it.
Can AI be trusted to classify regulated email?
AI works best alongside fixed rules, with confidence thresholds and human review for uncertain results. Every AI decision should also be logged so it can be explained later.
How long does implementation take?
A phased rollout usually runs about 90 days from scoping to enforcement, depending on environment complexity.
Does it replace DLP?
No. It complements DLP by adding policy workflow and a defensible audit trail.
How long should business email be retained?
It depends on the regulation and record type. Requirements range from a few years to seven or more, so confirm the schedule with your legal team.
See how it works in your environment
If you are evaluating compliance platforms, explore the MailGovern email compliance software overview or book a technical demo to see an audit trail generated from your own message workflows.